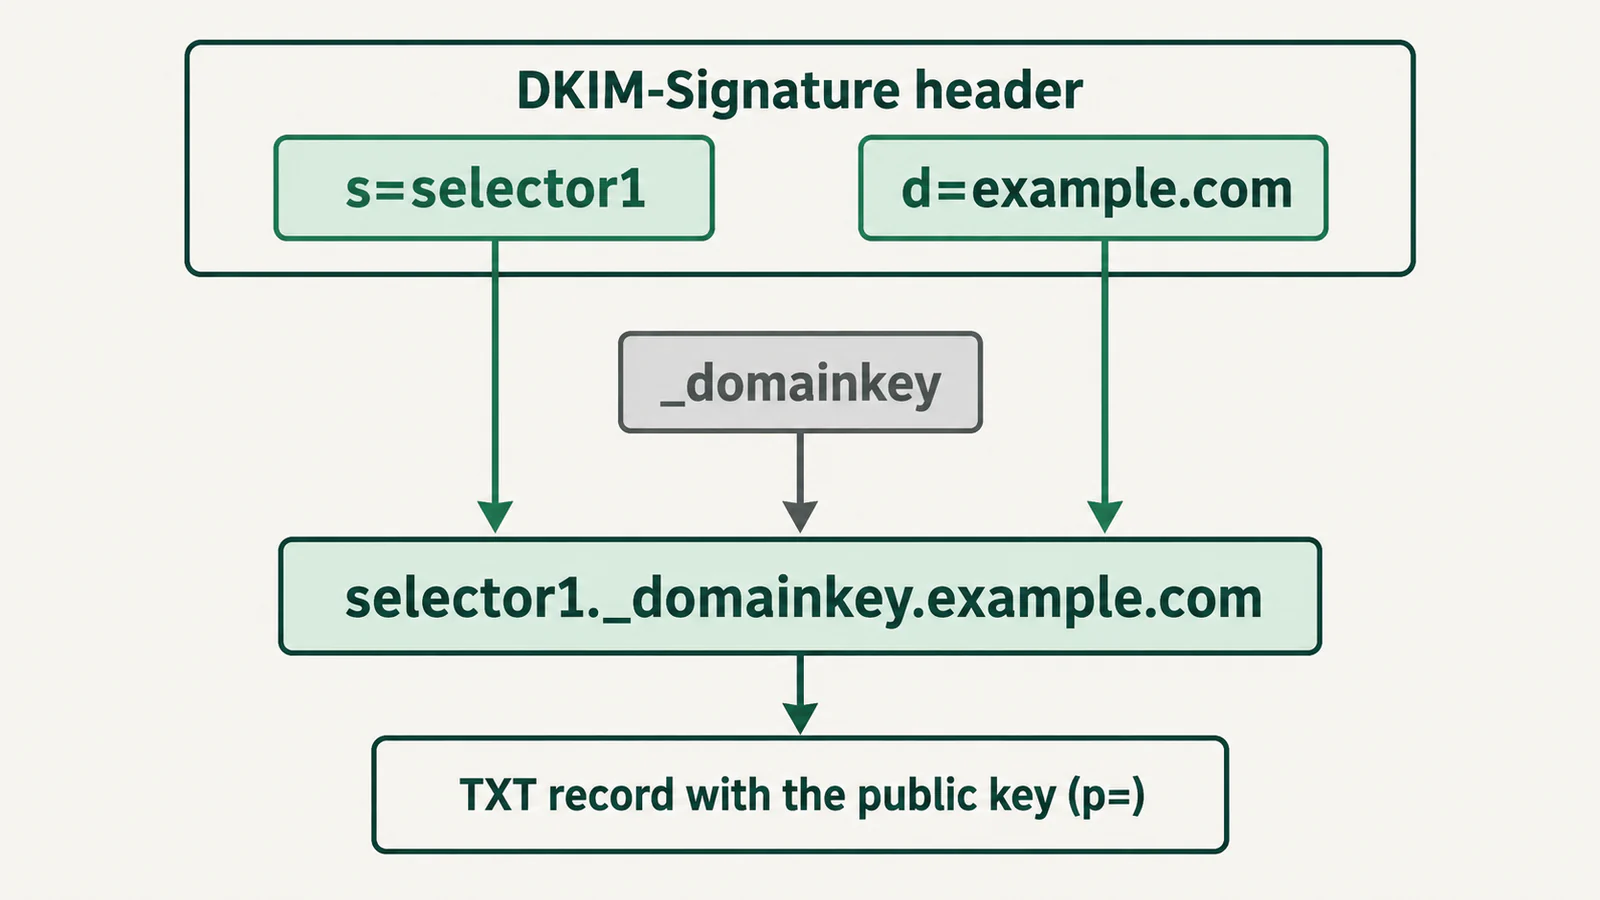
A DKIM selector is the value of the s= tag in a message's DKIM-Signature header. Together with the signing domain in the d= tag, it tells the receiving mail server which DNS name holds the public key for that signature: the selector, then _domainkey, then the signing domain. RFC 6376 defines selectors as the way one signing domain can publish several public keys at the same time, which is why a domain usually has one selector per sending service and no single "DKIM record".
DKIM-Signature: v=1; a=rsa-sha256; d=example.com; s=selector1; ...

Receiver looks up:  selector1._domainkey.example.com
To find a selector, read the s= value in the DKIM-Signature header of a real message from that sender, or copy it from the sender's domain-authentication screen. It cannot be worked out from the domain name alone, because DNS does not list the names that exist under _domainkey.
Inbox Pulse checks the DMARC, SPF, MX, MTA-STS, TLS-RPT, and BIMI records for up to 25 domains. It does not check DKIM, because a DKIM lookup needs a selector taken from a real message. Use it for the records around DKIM, including the DMARC policy that decides how much DKIM alignment matters. The free 10-domain audit covers SSL, DNS, and domain expiry for the same domains, and how CertPilot checks domains explains the limits of public DNS checks.
In short
- The selector is
s=, the signing domain isd=, and the key lives ats._domainkey.din DNS. - A domain can have many selectors: one per sender, plus an old and a new key during rotation.
- Find the selector in a real message header or in the sender's admin screen. A list of common selectors is a starting point, not proof.
- The record at that name is a TXT key record, or a CNAME that leads to one.
- DKIM passing is not DMARC passing. The
d=domain also has to align with the visible From domain.
How a DKIM selector works
- The sending platform signs the message with a private key and adds a
DKIM-Signatureheader. Two of its required tags ared=, the signing domain, ands=, the selector (RFC 6376 section 3.5). - The receiver joins the selector, the fixed label
_domainkey, and the signing domain into one DNS name (section 3.6.2.1). - It requests the TXT record at that name and reads the public key from the record's
p=tag. - It uses that key to verify the signature.
A selector can contain periods. Each part becomes its own DNS label, so s=2026.mail with d=example.com is looked up at 2026.mail._domainkey.example.com.
Selectors exist so keys can be separated and replaced. Each sending service can sign with its own key under its own selector, and a key can be rotated by publishing a new selector, switching signing to it, and removing the old record once mail signed with the old key has been delivered.
The standard defines the key record as a TXT record. Many providers ask you to publish a CNAME at the selector name instead, pointing to a TXT record the provider hosts and rotates. Receivers follow the CNAME, so both work. Publish whichever record type the provider specifies.
How to find your DKIM selector
The reliable source is a message the system actually sent.
- Send a real message from the system you are checking to a mailbox you control.
- Open the raw message. Most mail clients have a "show original" or "view source" option.
- Find the
DKIM-Signatureheader and readd=ands=. A message can carry more than one signature, for example one from the provider's own domain and one from yours. Note each pair. - Build the DNS name and query it. Put the selector first, then
_domainkey, then the signing domain.
dig +short TXT selector1._domainkey.example.com
nslookup -type=TXT selector1._domainkey.example.com
A published key record normally starts with v=DKIM1 and carries the public key in p=. An empty p= means the key has been revoked (RFC 6376 section 3.6.1).
If you cannot send a test message, the sender's domain-authentication screen shows the selector and the exact record to publish. If the lookup returns nothing, work through the DKIM record not found guide.
Common DKIM selectors by provider
Use these as starting points and confirm each one in the provider's admin screen and in a real message header.
- Google Workspace: the default selector prefix is
google, published as a TXT record atgoogle._domainkey. See Google's DKIM setup guide. - Microsoft 365:
selector1andselector2, published as two CNAME records atselector1._domainkeyandselector2._domainkey. Only one is active at a time; the other is used after a key rotation. See Microsoft's DKIM configuration guide. - Twilio SendGrid:
s1ands2as CNAME records when automated security is on, or a TXT record atm1._domainkeywhen it is off. A custom selector can be set during domain authentication. See SendGrid's domain authentication guide. - Mailchimp: two CNAME records whose names and values are issued in the account's authentication instructions. See Mailchimp's domain authentication guide.
- Amazon SES: with Easy DKIM, the DKIM records are generated by SES and shown in the SES console for the domain identity. See Amazon's Easy DKIM guide.
- Other platforms: Mailgun, Postmark, Klaviyo, HubSpot, Salesforce, helpdesks, and website SMTP plugins use generated or account-specific selectors. Copy the record from the platform's domain-authentication screen, not from a list.
Providers change their defaults, and an admin can often choose a custom selector. Treat every entry above as "likely", then verify it.
Common selector mistakes
- Checking the wrong selector. DNS has a record for
google, but the sender signs withselector1. The lookup for the wrong name fails even though DKIM is configured. - Publishing in the wrong place. The record is added under
www, with the domain doubled in the host field, or at a DNS provider that is not authoritative for the domain. - Using the wrong record type. The provider expects a CNAME and a TXT record is published, or the other way round.
- Leaving a retired sender's record behind. The record still resolves, which makes an audit look healthier than the sending setup is.
- Passing DKIM with the provider's domain. The message is signed with
d=set to the platform's domain, not yours. DKIM passes but does not help DMARC.
Why a selector list is not a sender inventory
Finding a DKIM record in DNS shows that one key is published. It does not show every system that sends mail for the domain. A client can have working DKIM for Google Workspace and still fail DMARC for marketing mail, invoices, password resets, or helpdesk replies.
Pair selector checks with a list of sending sources: the mailbox platform, marketing automation, transactional email, ecommerce, CRM, helpdesk, website forms, billing tools, and any legacy system still sending from the domain. A sender nobody can name turns DKIM troubleshooting into guesswork.
Record the selector for each sender
Keep a short record per sending source so the discovery work is done once:
- Sender: the platform or system.
- Visible From domain: the domain recipients see.
- Signing domain and selector: the
d=ands=values from a real message. - DNS record: the full name and whether it is TXT or CNAME.
- Evidence: message header, sender dashboard, or DNS lookup, with the date.
- Alignment note: whether the signing domain aligns with the From domain.
- Owner: who can change the sender's setup.
In client reports, name what was verified. "Google Workspace DKIM passed for the tested mailbox message" is accurate. "DKIM is fixed" is not, unless every sender was checked.
When to review selectors
Review selectors whenever the sending setup or DNS changes:
- a new marketing, CRM, ecommerce, or helpdesk platform starts sending;
- a provider rotates keys or a platform is retired;
- the primary domain or From address changes;
- a DMARC policy is about to move from monitoring toward enforcement;
- DNS moves to a new provider.
DNS migrations deserve extra care. Records under _domainkey are easy to miss when a zone is copied by hand, and the gap only shows when signed mail starts failing. The DNS drift guide covers how unplanned record changes are caught.
DKIM selectors and DMARC
DMARC does not look at selectors. It looks at whether a passing DKIM signature's d= domain aligns with the visible From domain (RFC 9989 section 4.4). A correct selector with the wrong signing domain still leaves DMARC depending on SPF.
For how the three mechanisms fit together, read DMARC, SPF, and DKIM explained for agencies. If the client sends at volume, the Google bulk sender DMARC checklist covers what Google expects from bulk senders, and the email authentication guide for agencies connects DKIM to the other DNS records, including the MTA-STS record check.
What CertPilot does and does not do here
CertPilot checks public email-authentication DNS records for monitored domains: MX, SPF, DMARC, MTA-STS, TLS-RPT, and BIMI. External Footprint Monitoring also lets you record each email sending source for a domain, with its owner, sending method, your own SPF, DKIM, and DMARC status, notes, and last-reviewed date. That is a practical home for the per-sender selector record above, and it feeds the Domain Health reporting workflow.
CertPilot does not look up DKIM selectors, read mailboxes or message headers, configure sender dashboards, rotate DKIM keys, send email, or guarantee deliverability. The sending-source record holds what you verified; it does not verify it for you.
Frequently Asked Questions
What is a DKIM selector?
A DKIM selector is the s= value in a message's DKIM-Signature header. Combined with the signing domain in d=, it forms the DNS name where the receiver finds the public key: selector, then _domainkey, then the domain. It lets one domain publish several keys at once.
How do I find my DKIM selector?
Send a message from the system in question, open the raw message, and read the s= tag in the DKIM-Signature header. The sender's domain-authentication screen shows the same value. A selector cannot be looked up from the domain name alone, because DNS does not list the names under _domainkey.
Can a domain have more than one DKIM selector?
Yes. Each sending service normally has its own selector and key, and a key rotation publishes a new selector beside the old one for a while. Many selectors on one domain is normal and is not an error.
Are DKIM selectors the same for every Google or Microsoft account?
Often, but not always. Google Workspace defaults to google and Microsoft 365 uses selector1 and selector2, yet an admin can choose a different Google prefix and Microsoft's CNAME targets are specific to each organization. Confirm in the admin screen and in a real message.
Is the s= tag in a DKIM DNS record the selector?
No. In the DKIM-Signature header, s= is the selector. Inside the DNS key record, an optional s= tag means service type, which is a different setting. The selector never appears inside the key record; it is part of the record's name.