Multiple SPF records means one hostname publishes two or more DNS TXT records that begin with v=spf1. That is not a stronger setup, and receivers do not merge the records for you. RFC 7208 says a domain name must not have multiple SPF records, and a receiver that finds more than one returns a permerror instead of evaluating either policy. The fix is to merge every confirmed sender into one SPF record, delete the duplicates in the same change, and confirm the merged record stays within SPF's limit of 10 DNS lookups.
Using several sending services is normal and is not the problem. Google Workspace, a CRM, and a transactional email provider can all be authorized inside one record with separate include: mechanisms. Other TXT records at the same name, such as site-verification strings, are also fine: SPF discards any record that does not start with v=spf1.
Use Inbox Pulse to check up to 25 domains for their visible SPF and DMARC records; it flags a domain when more than one v=spf1 record is published. Use the free 10-domain audit when you also need SSL, DNS, and domain expiry context, and read how CertPilot checks domains for what public DNS checks can and cannot show.
In short
- One hostname gets one
v=spf1record. RFC 7208 section 3 states that multiple SPF records are not permitted for the same owner name. - Two or more records produce a
permerror(section 4.5). SPF does not pass, so DMARC has to rely on aligned DKIM for that mail. - Receivers never combine the records. Someone with DNS access has to.
- Several
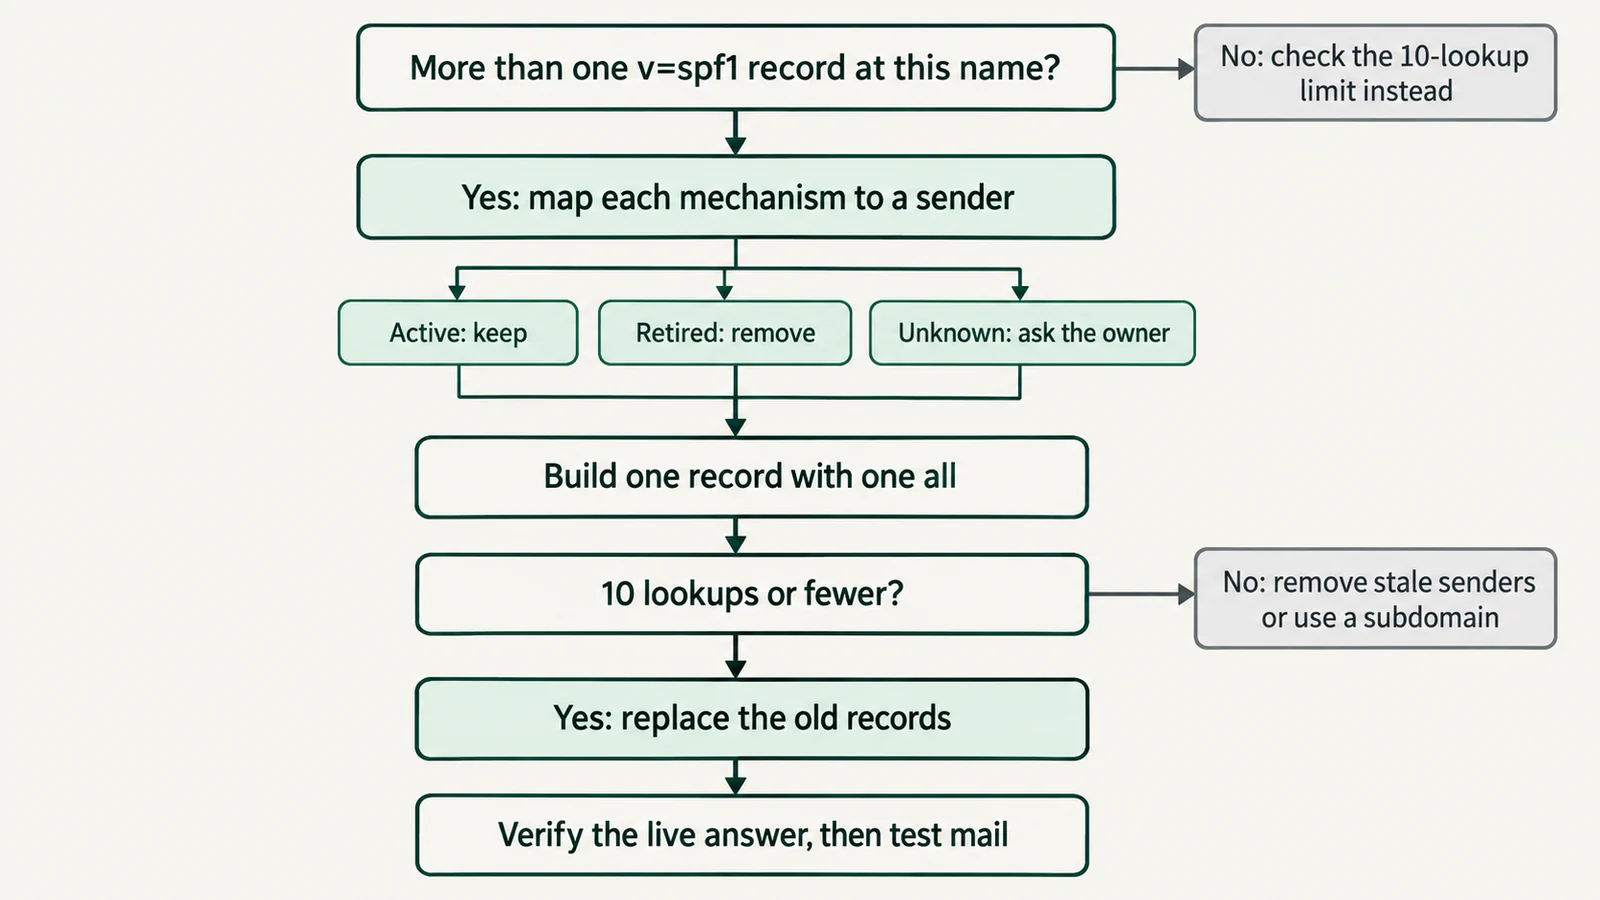
include:mechanisms inside one record are valid, as long as the record stays within 10 DNS-querying terms (section 4.6.4). - Fix order: list the records, map each mechanism to a sender, build one record, count lookups, replace the old records, verify the live answer, then test real mail.
What counts as multiple SPF records
The problem looks like this: two TXT records at the same name, each starting with v=spf1.
example.com.  TXT  "v=spf1 include:_spf.google.com -all"
example.com.  TXT  "v=spf1 include:sendgrid.net -all"
These are not two policies that get added together. Each one is a complete SPF policy, and SPF allows only one per name.
Several things look similar but are not the same problem:
- One record with several includes.
v=spf1 include:_spf.google.com include:sendgrid.net -allis a single policy. It is valid if the lookup limit is respected. - One record split into quoted strings. A long record can be stored as several character-strings inside one TXT record, and a DNS tool may show it as
"v=spf1 include:_spf.google.com " "include:sendgrid.net -all". Receivers join the strings without adding spaces (RFC 7208 section 3.3). That is still one record. - SPF records on different hostnames.
example.comandmail.example.comcan each publish their own record. SPF is checked for the exact name used as the envelope sender (MAIL FROM) or HELO domain, so each name is evaluated on its own. - Other TXT records at the same name. Verification strings for Google, Microsoft, or SaaS tools can sit beside the SPF record.
- A record of type SPF. Some DNS hosts still offer a dedicated SPF record type. RFC 7208 discontinued it: SPF policies are published as TXT records only.
Why receivers return a PermError
RFC 7208 defines how a receiver selects the record to evaluate. It looks up the TXT records at the name, discards the ones that do not begin with exactly v=spf1, and counts what is left (section 4.5):
- No record left: the result is
none. - Exactly one record: that record is evaluated.
- More than one record: the result is
permerror.
The standard describes permerror as meaning the domain's published records could not be correctly interpreted, an error condition that needs the DNS operator to step in (section 2.6.7). The receiver does not pick the newer record, the longer record, or the first one returned.
What a receiver does with a message after a permerror is its own local policy. The certain part is that SPF did not pass. That removes SPF as an authentication signal for every sender using the domain, including the ones whose mechanisms are listed correctly.
How to fix multiple SPF records
Start by reading what is live. Either command lists the TXT records at a name:
dig +short TXT example.com
nslookup -type=TXT example.com
Then work through these steps in order. The goal is one accurate record, not just one record.
- Count the SPF records. Look only at the answers that start with
v=spf1. Two or more at the same name is the problem this guide covers. - Confirm they share a hostname. A record at
example.comand one atmail.example.comare not duplicates. - Map every mechanism to a sender. For each
include:,ip4:,ip6:,a, andmx, write down which platform it authorizes and who owns that platform. - Decide what stays. Keep mechanisms for senders that are confirmed active. Remove the ones confirmed retired. Hold unknown ones until the domain owner answers, and do not delete an unknown sender during a live campaign.
- Build one record. Start with a single
v=spf1, add each confirmed mechanism once, and end with oneallmechanism. Keep the qualifier the domain already uses (-allor~all) unless the owner has decided to change it. - Count the lookups.
include,a,mx,ptr,exists, andredirecteach cause DNS queries, including the ones nested inside an included record. More than 10 produces apermerrorof its own. - Replace, do not add. Publish the merged record and delete every other
v=spf1record at that name in the same change. Adding the merged record beside the old ones leaves the error in place. - Verify and test. Query the domain's authoritative nameserver and confirm exactly one
v=spf1record is returned. Then send a message from each sending platform to a mailbox you control and read theAuthentication-Resultsheader forspf=pass.
Keep the previous values in the ticket so the change can be rolled back. A DNS dashboard can show a saved record that is not live yet, or the domain may use different nameservers than expected, so trust the query result over the dashboard.
Example: merging two records
Before:
v=spf1 include:_spf.google.com -all
v=spf1 include:sendgrid.net include:mailgun.org -all
After:
v=spf1 include:_spf.google.com include:sendgrid.net include:mailgun.org -all
This shows the shape, not a recommendation. Someone still has to confirm that Google, SendGrid, and Mailgun all send mail for the domain today. If Mailgun was retired two years ago, copying it into the merged record keeps an unused sender authorized.
Multiple includes are fine, within the lookup limit
A vendor setup screen that says "add this SPF record" almost always means "add this include: to the record you already have." Creating a second full record is the most common way duplicates start.
One record can hold many includes, but each one costs DNS lookups, and an included record can contain further includes. Check the total before publishing with the SPF 10 lookup limit debugging guide.
SPF flattening, which replaces includes with lists of IP addresses, lowers the lookup count but creates a maintenance duty. Providers change their sending addresses, and a flattened record that nobody updates will start failing legitimate mail. Removing retired senders or moving one sender to its own subdomain is usually the safer first move.
Why duplicate SPF records appear
Duplicates are usually a process problem, not a technical mystery:
- Vendor instructions: a platform's "add this record" step is followed literally.
- DNS migration: records are copied to a new provider and then added again by hand.
- Old platforms: a retired newsletter, CRM, or helpdesk record is never removed.
- Split ownership: marketing or a contractor adds a sender without seeing the existing record.
- Root and subdomain confusion: a sender meant for a subdomain is added at the root.
This is why the sender list comes before the DNS edit. If nobody knows which platforms send mail, cleaning up SPF can break legitimate email.
Subdomains and dedicated sending domains
Not every sender has to be authorized at the root domain. Marketing mail from news.example.com or transactional mail from mail.example.com can use that hostname's own SPF record, which keeps the root record short.
This only works when the platform is configured to use the subdomain as its envelope sender. Moving an include to a subdomain the platform does not use changes nothing. Each sending subdomain also needs its own DKIM and DMARC review.
How duplicate SPF records affect DMARC
DMARC passes when either SPF or DKIM passes and is aligned with the visible From domain (RFC 9989 section 4.4). When duplicate records turn SPF into a permerror, only DKIM is left.
That is harmless for a sender with aligned DKIM and a failure for a sender that relied on SPF. A newsletter platform with DKIM configured keeps passing, while a CRM that was never given a DKIM key starts failing DMARC. Treat SPF cleanup as part of one SPF, DKIM, and DMARC review; DMARC, SPF, and DKIM explained for agencies covers how the three fit together.
If the domain already receives aggregate reports, they can show which senders were affected and whether they recover after the merge. Reports do not fix duplicate records, and one report is not a complete sender list. Keep the DNS fix separate from DMARC RUA and RUF report ownership, and do not tighten the DMARC policy just because the SPF records were merged.
Change request when you do not control DNS
When the client or another vendor owns DNS, send a request that cannot be misread:
Please replace the existing SPF TXT records at example.com with one TXT record:

Host: @
Type: TXT
Value: v=spf1 include:_spf.google.com include:sendgrid.net -all

Do not add this as a second SPF record. It must replace the existing
records that begin with v=spf1.
Add the reason in one sentence: the domain currently publishes more than one SPF record, receivers accept only one, and the duplicates cause an SPF error for all mail from the domain.
What CertPilot does and does not do here
Inbox Pulse reads public DNS for up to 25 domains and reports whether SPF is present, missing, or published more than once, along with the visible DMARC, MX, MTA-STS, TLS-RPT, and BIMI records. External Footprint Monitoring checks the same public email-authentication records for monitored domains and lets you record each sending source with its owner, so the sender list from step 3 has a home.
CertPilot does not edit DNS, merge SPF records, read mailboxes or message headers, or guarantee deliverability. It does not process DMARC aggregate reports; the RUA and RUF guide explains what those reports cover and who should own them. It does not check DKIM, because a DKIM lookup needs a selector from a real message.
For the wider workflow, see the email authentication guide for agencies and bulk DMARC checks for client domains.
Frequently Asked Questions
Can you have more than one SPF record?
No. A hostname can have only one TXT record that starts with v=spf1. RFC 7208 does not permit multiple SPF records for the same name, and receivers return a permerror when they find more than one. A domain can still have many other TXT records, and different hostnames can each have their own SPF record.
What is the difference between multiple SPF records and multiple includes?
Multiple SPF records are separate TXT records that each start with v=spf1, which is an error. Multiple includes are several include: mechanisms inside one record, which is valid. One record can authorize Google Workspace, a CRM, and a transactional provider together, provided the total stays within the 10 DNS lookup limit.
Which SPF record do receivers use when there are two?
Neither. The standard does not tell receivers to choose the first, the newest, or the longest record. Finding more than one SPF record produces a permerror, and no SPF policy is evaluated for the message.
How do you merge SPF records?
List every v=spf1 record at the name, identify the sender behind each mechanism, drop retired senders, and build one record with each confirmed mechanism once and a single all at the end. Count the DNS lookups, replace the old records with the merged one in the same change, then confirm the live answer and test mail from each platform.
Will fixing multiple SPF records fix deliverability?
It removes one authentication failure. It does not guarantee inbox placement, which also depends on DKIM, DMARC alignment, sender reputation, complaints, and content. Treat the merge as one part of an email-authentication review.