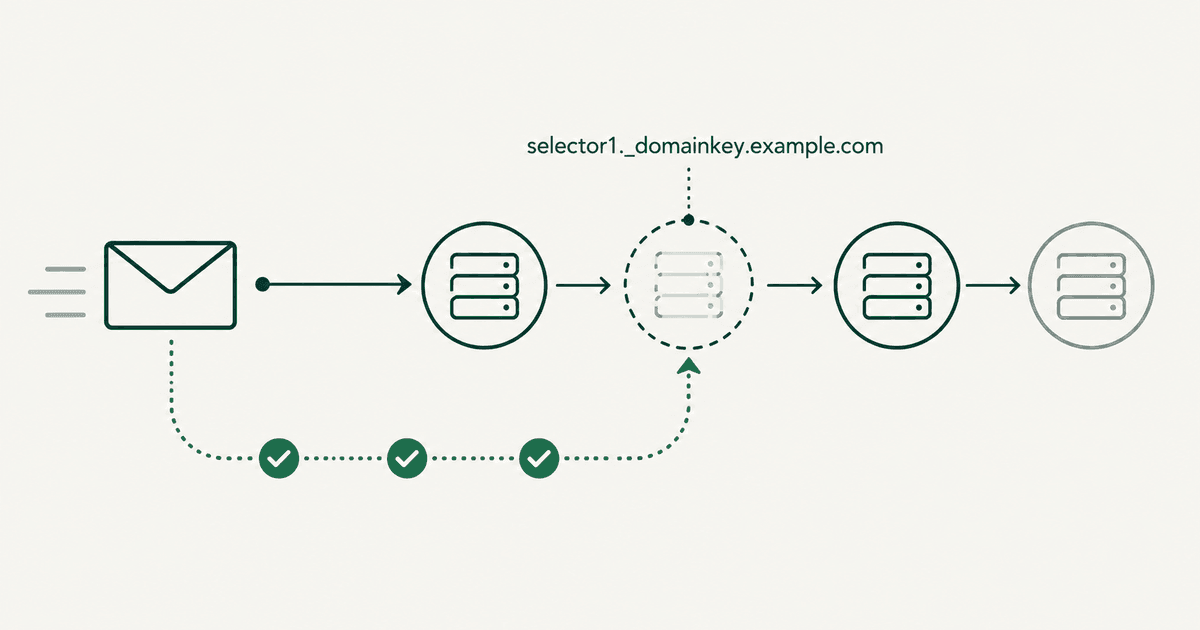
DKIM record not found means a lookup for a DKIM public key returned nothing usable at one specific DNS name: the selector, then _domainkey, then the signing domain. The result is about that one selector and that one domain. It does not prove DKIM is missing for the whole domain, and it does not prove mail is being blocked. The usual causes are a checker that tried a selector the sender does not use, a record that was never published or sits under the wrong name or in the wrong DNS zone, and DKIM signing that was never switched on in the sending platform.
The fix starts with a real message, not with a guess. The DKIM-Signature header of a message the sender actually sent contains the signing domain (d=) and the selector (s=). Those two values give the exact DNS name to check, and every later step depends on them.
Inbox Pulse checks the DMARC, SPF, MX, MTA-STS, TLS-RPT, and BIMI records for up to 25 domains. It does not check DKIM, because a DKIM lookup needs a selector from a real message. Use it to see the DMARC policy and SPF record that sit around the DKIM problem, use the free 10-domain audit for SSL, DNS, and domain expiry context, and read how CertPilot checks domains for what public DNS checks cover.
In short
- A DKIM lookup targets one name:
selector._domainkey.domain. No record at that name is what "not found" means. - A tool that knows only the domain has to guess selectors. A scanner reporting no DKIM record may simply not have tried yours.
- Read
d=ands=from a real message first. Then build the name, query it, and check where the record was published. - If the name is right and the record is missing, publish the exact record the sending platform shows and make sure signing is switched on there.
- Finish by sending another message and reading the result, then check DMARC alignment.
What the error is checking
DKIM does not have one record per domain. Each sending service signs with its own key, and each key is published under its own selector. RFC 6376 defines the lookup: for a signature with d=example.com and s=selector1, the receiver queries selector1._domainkey.example.com.
When a receiving mail server finds no key record at that name, the standard tells it to treat that signature as a permanent failure with the reason "no key for signature" (section 6.1.2). The message is not automatically rejected. It simply has no valid DKIM signature from that key, so DMARC has to rely on SPF.
The DKIM selector guide explains selectors in more detail and lists common provider defaults.
Diagnose it in this order
- Confirm the signing domain. Send a message from the affected system to a mailbox you control, open the raw message, and find the
DKIM-Signatureheader. Thed=tag is the signing domain. If it shows the provider's domain instead of yours, the key lives in the provider's DNS and there is nothing missing from your zone until custom-domain signing is set up. - Find the selector. The
s=tag in the same header is the selector. If there is noDKIM-Signatureheader at all, the platform is not signing, and the problem is in the platform settings (step 6), not in DNS. - Build the DNS name. Selector first, then
_domainkey, then the signing domain:selector1._domainkey.example.com. - Query the record. Ask for the TXT record at that exact name. The commands are below.
- Check where it was published. If nothing comes back, confirm which nameservers are authoritative for the domain and that the record was added there, under the right host name and with the record type the provider asked for.
- Check the provider configuration. Confirm that DKIM signing is enabled for this domain in the sending platform, not only that the DNS records were listed.
- Retest with a real message. Send again and read the
Authentication-Resultsheader for the DKIM result and the domain it was evaluated for.
dig +short TXT selector1._domainkey.example.com
nslookup -type=TXT selector1._domainkey.example.com

dig +short NS example.com
The first two commands query the key record. The third lists the domain's nameservers, which tells you which DNS provider actually answers for the domain.
What the lookup result means
- No such name, or an empty answer. Nothing is published at that name where resolvers can see it. Continue with steps 5 and 6.
- A CNAME that leads nowhere. The CNAME exists but its target has no TXT record. The sending platform has not finished setup, or the CNAME value was copied incorrectly.
- A TXT record with a
p=value. The key is published. If a tool still says "not found", it checked a different selector or a different domain. - A TXT record with an empty
p=. The key has been revoked (RFC 6376 section 3.6.1). Signatures made with it fail. The sender needs a current key. - Two TXT records at the same selector name. The standard requires one key record per selector name and calls the result of several undefined (section 3.6.2.2). Remove the stale one.
Publication problems to check
Most missing records were published, just not where the lookup looks.
- Wrong DNS provider. The record was added at a provider that is no longer authoritative, often after a nameserver change or a migration.
- Doubled domain in the host field. Many DNS panels append the domain automatically. Entering the full name creates
selector1._domainkey.example.com.example.com. - Wrong level. The record was added under
wwwor another subdomain, or at the root domain when the sender signs for a subdomain. - Wrong record type. The platform asked for a CNAME and a TXT record was created, or the other way round. Microsoft 365 uses two CNAME records,
selector1._domainkeyandselector2._domainkey, and only one selector is active at a time, so the second can look unused until a key rotation (Microsoft's DKIM guide). - Altered value. The key was truncated, wrapped in extra quotes, or pasted with a line break in the middle.
- Not live yet. DNS changes are not instant. Google says DKIM authentication can take up to 48 hours to start working after the key is added (Google's DKIM setup guide).
Do not overwrite an existing record at a selector name to "fix" a different sender. Each sender has its own selector, and replacing one breaks the service that uses it.
Provider configuration to check
A published record does nothing until the platform signs with the matching key.
- Is signing enabled for this domain? Google Workspace needs the admin to start authentication after the TXT record is added. Microsoft 365 needs DKIM signing enabled for the custom domain after the CNAME records are detected.
- Is the platform signing with your domain? Some platforms sign with their own domain until custom-domain authentication is completed. DKIM then passes for the provider's domain and does nothing for DMARC on yours.
- Is the sender still in use? If the warning comes from a retired platform, the right fix is to remove its records and stop it sending, not to publish a new key.
These checks need admin access to the sending platform. When the agency does not have it, ask the client for the domain-authentication screen and name the person who can change it.
Why DKIM can be missing while SPF and DMARC exist
SPF, DKIM, and DMARC are separate DNS records that do not create each other. A domain can publish SPF at the root and a DMARC record at _dmarc.example.com while one of its senders has no DKIM key at all.
This is common after a migration. A client moves mail platforms or DNS hosts, the old SPF and DMARC records carry over, and the new platform's DKIM record is never published. DMARC, SPF, and DKIM explained for agencies covers how the three work together.
If the client receives DMARC aggregate reports, they can show how much mail the affected sender handles and whether SPF alignment is covering it in the meantime. Reports help with priority; they do not replace confirming the sender and selector. The DMARC RUA and RUF guide explains what those reports contain.
What to record once it is fixed
Write the result down per sender so the next audit does not start from zero:
- Sender: the platform that signs the mail.
- Signing domain and selector: the
d=ands=values from the test message. - DNS record: the full name, TXT or CNAME, and the DNS provider that hosts it.
- Status and evidence: passing, pending, or retired, with the date and what was checked.
- Owner: who can change the DNS record and who can change the sender's settings.
When reporting to a client, describe what was found, not a verdict. "One sending platform has no published DKIM key; we are confirming the selector with the platform owner" is accurate. "Your email is broken" usually is not.
What CertPilot does and does not do here
CertPilot checks public email-authentication DNS records for monitored domains: MX, SPF, DMARC, MTA-STS, TLS-RPT, and BIMI. External Footprint Monitoring also lets you record each email sending source for a domain with its owner, your own SPF, DKIM, and DMARC status, notes, and last-reviewed date, which is where the per-sender record above can live.
CertPilot does not look up DKIM selectors, read mailboxes or message headers, send test email, publish or change DNS records, process DMARC aggregate reports, or guarantee deliverability. For the wider workflow across all the email DNS records, see the email authentication guide for agencies.
Frequently Asked Questions
What does DKIM record not found mean?
It means no usable DKIM key record was returned for one selector and one signing domain, at a name like selector1._domainkey.example.com. It describes that single lookup. Other senders on the same domain can have working DKIM under different selectors.
Why does a checker say no DKIM record found when DKIM is working?
Because the checker did not know the selector. DNS does not list the names under _domainkey, so a tool given only a domain has to try common selectors. If the sender uses a different one, the tool reports nothing even though signed mail passes. Check the DKIM-Signature header of a real message to see the selector in use.
How do I know which DKIM selector to check?
Read the s= tag in the DKIM-Signature header of a message from that sender, or look at the sending platform's domain-authentication screen. Lists of common selectors help with orientation, but only the message or the platform shows the one actually in use.
Can a domain pass SPF and still have DKIM missing?
Yes. SPF and DKIM are separate. A domain can authorize its sending servers in SPF while a marketing platform, CRM, or transactional sender has no DKIM key published. DMARC can still pass for that mail through aligned SPF, but the sender has no second signal if SPF fails or mail is forwarded.
Should an agency add a DKIM record without platform access?
Only when the platform has supplied the exact record. Guessing a selector does not fix the sender, and overwriting an existing record can break another service. If the client owns the sending account or DNS, send them the exact host name, record type, and value, and record who made the change.